Blockchain · Explainer
Four ways to hold digital assets—and what each leaves exposed
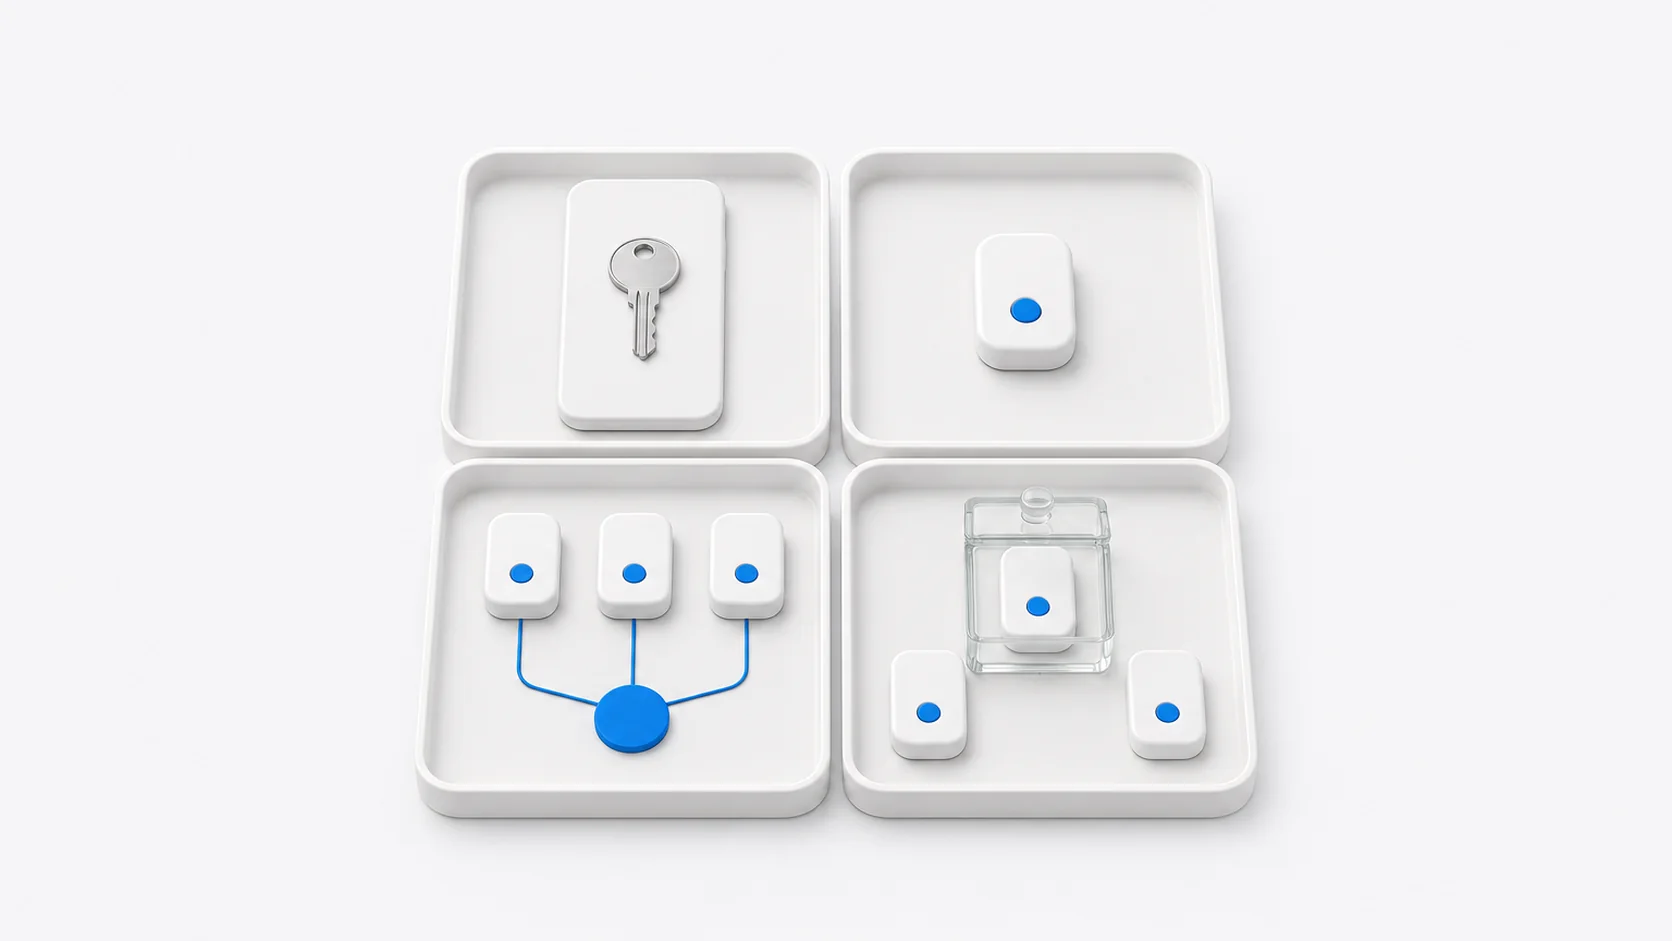
When explaining digital-asset custody, I start with a question that sounds simple: who can move the assets?
The answer becomes more interesting when a phone is stolen, a signing device stops working, or the person responsible is unavailable. A setup that works beautifully on an ordinary day may become difficult to operate under those conditions.
Software wallets, hardware wallets and multi-party computation offer different ways to organise control. Putting them in a sequence helps explain the differences. Treating that sequence as a universal safety ranking hides too much.
1. A software wallet on an everyday device
In this example, your phone or computer holds the material needed to sign a transaction. The wallet is convenient because the device you already use can authorise a transfer.
That convenience also concentrates responsibility. If an attacker obtains usable signing material, they may be able to authorise transfers. If the device fails and you have no usable recovery route, access may be lost.
A mnemonic, often called a seed phrase, represents recovery information. It does not have to sit on the same device as the wallet. Keeping the only copy there would link two failures: losing the device and losing the backup.
The useful question is: what could compromise both my normal access and my recovery route?
2. A separate hardware signer
A hardware signer separates signing from the everyday computer or phone. Transaction data reaches the device; in normal signing, it produces a signature without handing the private key to the connected computer.
Bluetooth is one way to transport that data. USB and optical transfer are others. The transport alone does not tell you whether a transaction is sensible or whether the device displays enough information to verify it. Ledger's explanation of the Nano X Bluetooth security model describes one implementation of this separation.
The downside is easy to miss: a protected key can still sign a harmful request. Key isolation and approval quality solve different problems. Recovery material also remains a route to control; protecting the device while exposing the complete backup leaves a serious gap.
3. Several participants sign together
Threshold signing distributes the operation across participants. For example, a two-of-three arrangement requires two participants to cooperate. Suitable protocols can produce a signature using shares without reconstructing the complete private key on one device. This is part of the field described by NIST's threshold cryptography project.
The attractive property is that compromising one share need not be enough to sign. In this illustrative two-of-three arrangement, losing one participant also need not stop ordinary signing.
But count control, not just devices. Three devices under one compromised administrator can share a common failure. Key generation, imports, backups and recovery procedures also need examination. The label “MPC” does not answer those questions by itself.
4. Require an offline participant
An offline signing device reduces its direct network exposure. The important word is require.
Imagine three shares: two online and one offline. If any two can sign, the online pair can complete a transaction without the offline device. Merely having an offline share does not make it part of every approval.
Now imagine two shares, with both required and one kept offline. The online participant alone cannot meet that threshold. The operational cost is equally clear: if the offline signer is unavailable, ordinary signing stops until access is restored or an authorised recovery procedure succeeds.
These are fictional arrangements for understanding the trade-off, not product security assessments. An offline device still processes information and can approve the wrong transaction.
Draw the failure before choosing the design
For each arrangement, I would put three questions beside the diagram:
- Who must cooperate to move assets?
- What happens when a required person or device is unavailable?
- Who can use the recovery route, and what evidence or authority do they need?
Technical signing control and legal entitlement are separate questions. A workable handover needs both addressed.
You can compare the four designs in the interactive guide. Keep one failure selected while changing the design. Watch which exposure decreases—and which new responsibility appears.